Malware Archive
Tenda routers found with hidden authentication backdoor allowing full admin access
A newly disclosed security vulnerability affecting multiple Tenda router firmware versions has revealed the presence of a hidden authentication backdoor capable of granting attackers full administrative access without requiring legitimate login credentials. The issue, tracked as CVE-2026-11405, was published by the CERT Coordination Center (CERT/CC) under Vulnerability
30 WordPress plugins compromised, someone planted a backdoor in all of them
The backdoor wasn’t a smash-and-grab. It wasn’t noisy, and it wasn’t rushed. It was planted quietly and left to sit for eight months before anyone flipped the switch. I traced the plugin’s history through 939 quicksave snapshots. The code tells a very specific story if you’re willing

Axios compromised on NPM – Malicious versions deploy cross-platform RAT
A highly sophisticated supply chain attack has struck one of the most widely used JavaScript libraries in the world. Two malicious versions of the popular HTTP client axios—1.14.1 and 0.30.4—were published to npm after a maintainer account was hijacked, introducing a stealthy remote access trojan (RAT) affecting

Notepad++ hijacked by state-sponsored actors
In a sobering reminder that even widely trusted open-source projects can become collateral damage in geopolitical cyber conflict, the Notepad++ project has confirmed a prolonged and highly targeted supply-chain attack that compromised its update delivery infrastructure. The incident, which unfolded quietly over several months in 2025, did
Critical security vulnerability in React Server Components enables unauthenticated RCE
The React Team has disclosed a critical security vulnerability affecting React Server Components that can allow unauthenticated remote code execution on affected servers. The issue is tracked as CVE-2025-55182 and carries a cvss score of 10.0, the highest possible severity rating. Developers using React Server Components are
Shai-Hulud Returns: Massive Supply-Chain Attack Infects 1K+ NPM Packages and 27K+ GitHub Repositories Within Hours
The notorious Shai-Hulud malware has resurfaced in one of the most aggressive software supply-chain attacks seen in the open-source ecosystem, compromising more than 1,000 npm packages and triggering a wave of over 27,000 malicious GitHub repositories in mere hours. The campaign abuses a fake Bun JavaScript runtime
Edward Snowden on FBI vs Apple
In Malware
In a recent Tweet, Edward Snowden says that there are some crucial details in the FBI vs Apple case being obscured by the officials. Below you can find a list with Snowden’s conclusions: 1. The FBI already has all of the suspect’s communications records — who they
From now on, you can watch videos on YouTube without advertising!
In Malware
Online video platform YouTube, a subsidiary of Google, announced Wednesday the launch of a subscription that allows users to watch videos without advertising, writes AFP. The offer will be launched in the US on October 28, priced at 9.99 dollars a month, the group said. YouTube said
Siri interrupted a press conference at the White House(video)
In Malware
Virtual Personal Assistant Siri, available on some Apple products, including mobile phones, has interrupted a session press inquiries held at the White House, answering to a journalist before he got to finish what he had to say, writes The Guardian. American journalist had asked the press
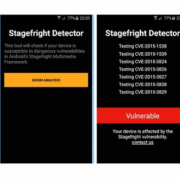
Stagefright Detector, a must have Android mobile application
In Malware
Stagefright is the worst nightmare that an Android owner can have. This is the android vulnerability discovered by Joshua J. Drake, from the Zimperium Mobile Security. I described this android vulnerability in an earlier post, called Critical Android phones Vulnerability. Stagefright spreads via MMS and once it