Bun Archive
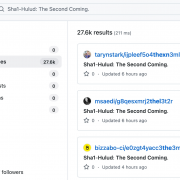
Shai-Hulud Returns: Massive Supply-Chain Attack Infects 1K+ NPM Packages and 27K+ GitHub Repositories Within Hours
The notorious Shai-Hulud malware has resurfaced in one of the most aggressive software supply-chain attacks seen in the open-source ecosystem, compromising more than 1,000 npm packages and triggering a wave of over 27,000 malicious GitHub repositories in mere hours. The campaign abuses a fake Bun JavaScript runtime